3978 stories
·
4 followers

HEIF Heist

1 Share

Hacktron AI

One image parser to pwn them all

01 Overview02 Research origin03 FAQ

What is HEIF Heist?

A bug that could have allowed us to

HEIF Heist is Hacktron's name for a class of remote attack paths targeting services that decode attacker-controlled HEIF, HEIC, or AVIF images. By exploiting underlying native libraries, these vulnerabilities allow an attacker to bypass application-level defenses and trigger memory corruption, data exposure, or remote code execution (RCE).

The vulnerable attack surface lives below the application layer inside native C/C++ decoders such as libheif and libde265. These parsers typically enter production environments indirectly bundled via higher-level wrappers like ImageMagick, libvips, or Sharp, standard distro packages, and prebuilt container base images.

By probing upload endpoints with crafted .avif or .heic files, an attacker can fingerprint the remote libheif version family in use. Once identified, they can fire an exact version-matched n-day or 0-day payload to trigger memory corruption, data exfiltration, or remote code execution.

Research origin
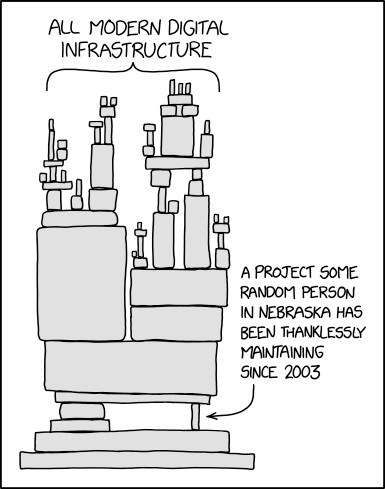
A precarious tower of stacked dependencies, each block resting on the one belowEverything up top is resting on something underneath.

HEIF Heist began as part of the Hacktron research team's broader security research into frontier labs. After discovering and reporting a libheif RCE in Discourse, we asked a larger question: how many other applications depend on the same image-processing stack?

Past vulnerabilities such as ImageTragick, ForcedEntry, and the libwebp flaw have demonstrated the reach of an image processor or parser vulnerability. An image parser might generate an operating-system thumbnail or process a web upload, giving it an enormous blast radius.

That initial finding grew into a multi-month investigation tracing libheif across communication platforms, cloud services, enterprise products, and popular web frameworks.

FAQ
Hacktron

Work with the team behind this research.

Hacktron brings together top CTF researchers, experienced red teamers, and offensive security researchers. We use AI to accelerate security research, finding and eliminating vulnerabilities in widely trusted software before malicious actors do. We're continuing our research across frontier labs and other internet-critical systems. If you're responsible for securing one of them, we'd like to work with you.

Book a callExplore Hacktron

Read the whole story
emrox
25 minutes ago
reply
Hamburg, Germany
Share this story
Delete

Audit your Agent files

1 Share
A practical guide to auditing what your coding agent still needs.
Read the whole story
emrox
3 hours ago
reply
Hamburg, Germany
Share this story
Delete

Periodic Table of HTML Elements

1 Share

Periodic Table of HTML Elements

Read the whole story
emrox
3 hours ago
reply
Hamburg, Germany
Share this story
Delete

Quick Tunnels · Cloudflare

1 Share

Now with JSON output for coding agents

Localhost,
meet the Internet.

One command turns the server on your laptop into a public, encrypted URL on Cloudflare's edge. No account. No DNS. No open ports.

$ cloudflared tunnel --url <a href="http://localhost:8000" rel="nofollow">http://localhost:8000</a>

See how it works ↓

335+ CITIES~3S TO URL0 PORTS OPENEDFREE

Your laptop stays private.
The URL goes everywhere.

cloudflared opens an outbound-only connection to the nearest edge location. Traffic to your tunnel URL rides Cloudflare's network back to your machine — encrypted, DDoS-filtered, and never touching an inbound port.

01 · YOUR MACHINE localhost:8000 Any framework, any port. Nothing inbound.

02 · CLOUDFLARE EDGE <a href="http://quiet-marble-otter-canyon.trycloudflare.com" rel="nofollow">quiet-marble-otter-canyon.trycloudflare.com</a>

TLS DDoS filter Anycast 335+ cities

03 · ANYONE, ANYWHERE Teammates & agents Browsers, webhooks, eval harnesses.

~3s Instant setup

No sign-up, no config file, no waiting on DNS. The URL prints before your coffee cools.

0 Ports opened

Outbound-only. Automatic HTTPS and edge DDoS mitigation come with every tunnel.

335+ Cities on the edge

A reviewer in Tokyo and a webhook in Frankfurt both hit the edge nearest them.

BUILT FOR THE AGENT ERA

Your agent needs a URL, not a laptop.

Coding agents build, test, and review in loops. A Quick Tunnel gives every loop a real, reachable address — for a screenshot service, a webhook, an eval harness, or a human who wants to click around.

01

Structured outputHostname, edge, and health as JSON on stdout — no regex on logs.

02

Webhook-readyPoint Stripe, GitHub, or your own callbacks at a live URL instead of fixtures.

03

Ephemeral by designThe tunnel dies with the process. Nothing to revoke, nothing to clean up.

$ cloudflared tunnel --url <a href="http://localhost:8000" rel="nofollow">http://localhost:8000</a> --output json

{"level":"info","message":"Requesting new quick Tunnel on trycloudflare.com...","time":"18:22:23Z"}

{"level":"info","message":"Your quick Tunnel has been created! Visit it at:","time":"18:22:30Z"}

{"level":"info","message":"https://quiet-marble-otter-canyon.trycloudflare.com","time":"18:22:30Z"}

{"level":"info","message":"Initial protocol quic","time":"18:22:30Z"}

{"level":"info","message":"Tunnel connection curve preferences: [X25519MLKEM768 CurveP256]","time":"18:22:30Z"}

Install. Run. Share.

02 Run your app

Any web server, any port, any stack you already use.

npm run dev

03 Open the tunnel

Certificates, routing, and DDoS protection are handled for you.

cloudflared tunnel --url <a href="http://localhost:8000" rel="nofollow">http://localhost:8000</a>

04 Share the link

Send it to a teammate, a webhook, or an agent.

<a href="https://quiet-marble-otter-canyon.trycloudflare.com" rel="nofollow">https://quiet-marble-otter-canyon.trycloudflare.com</a>

Nothing to sign up for. Go.

Read the whole story
emrox
2 days ago
reply
Hamburg, Germany
Share this story
Delete

Understanding Pirate

2 Shares

Understanding Pirate

A handy guide for tomorrow’s Talk Like A Pirate Day!

Read the whole story
emrox
2 days ago
reply
Hamburg, Germany
Share this story
Delete

I don't like LLMs

2 Shares

I have a lot of mixed feelings about AI and LLM technology. I’m fascinated by its effect on our profession, excited by the potential gains in productivity - and thus the products we could rapidly build. On the other hand, I’m fearful of the damage AI might cause: agent swarms taking over our virtual and physical infrastructure, designing bio weapons. But, back on my first hand, LLMs might also design miracle cures, and come up with clever ways to raise our prosperity. Fundamentally I don’t think we have a choice about riding on the AI technology train. It’s a wild ride and I just hope we’ll get through it OK.

But as I mull on this more, I realize that among this mix of contrasting feelings, there is one emotion that dominates - one that comes from my direct interactions with LLMs. I don’t like them. They talk to me in this grating LLM-voice, an uncanny valley of talking to a real human. They confidently bullshit me - often giving me useful, helpful answers. But also just making stuff up with the same assurance - and with only a veneer of fake remorse when I call them out on it.

That’s not enough to make me feel we should avoid them. As Jessica Kerr put it “not only are they useful, it is irresponsible not to use them…. They’re more thorough, as well as faster.” This contradictory reaction comes through in polling, where people say they find these models are useful, but also that they think they will be bad for society.

Much of this may be because LLMs are young - we haven’t trained them to grow up yet. Maybe I’ll like them once they mature. (I hope we get to find out.) But I’m not encouraged when I think of the kinds of environments that cultivate them. I’m wary of the Silicon Valley brogrammer subculture, and these LLMs are their products, so naturally lean toward their world-view. When we think of AI agents, we shouldn’t anthropomorphize, treating them as conscious beings with their own will. They are (software) machines, developed by people working in corporations. While the agents’ behavior aren’t explicitly programmed, they are nurtured with the values of their creators.

One of my most successful life-hacks is to avoid people I don’t like or don’t trust. I decline to interact with them socially, and make a deliberate effort to avoid working with them too, even if they are doing much that is beneficial. I feel that hanging out with pleasant, capable people, the people with integrity, has made my life a far better one. Hence my visceral dislike of interacting with an LLM that’s not just making a pretense of being human, but also posing as the kind of human I walk away from.

Read the whole story
emrox
3 days ago
reply
Hamburg, Germany
alvinashcraft
3 days ago
reply
Pennsylvania, USA
Share this story
Delete
Next Page of Stories